
Bray Lozano
Cybersecurity technician · Cantabria
I came from IT support, so I know the infrastructure I defend from the inside.
Chladni patterns. It is what a well written detection rule does, ordering the noise until the figure shows.
El Diario Montañés22 March 2026 · p. 44
I thought I would have to leave Cantabria to find an opportunity like this, and I see that is not the case
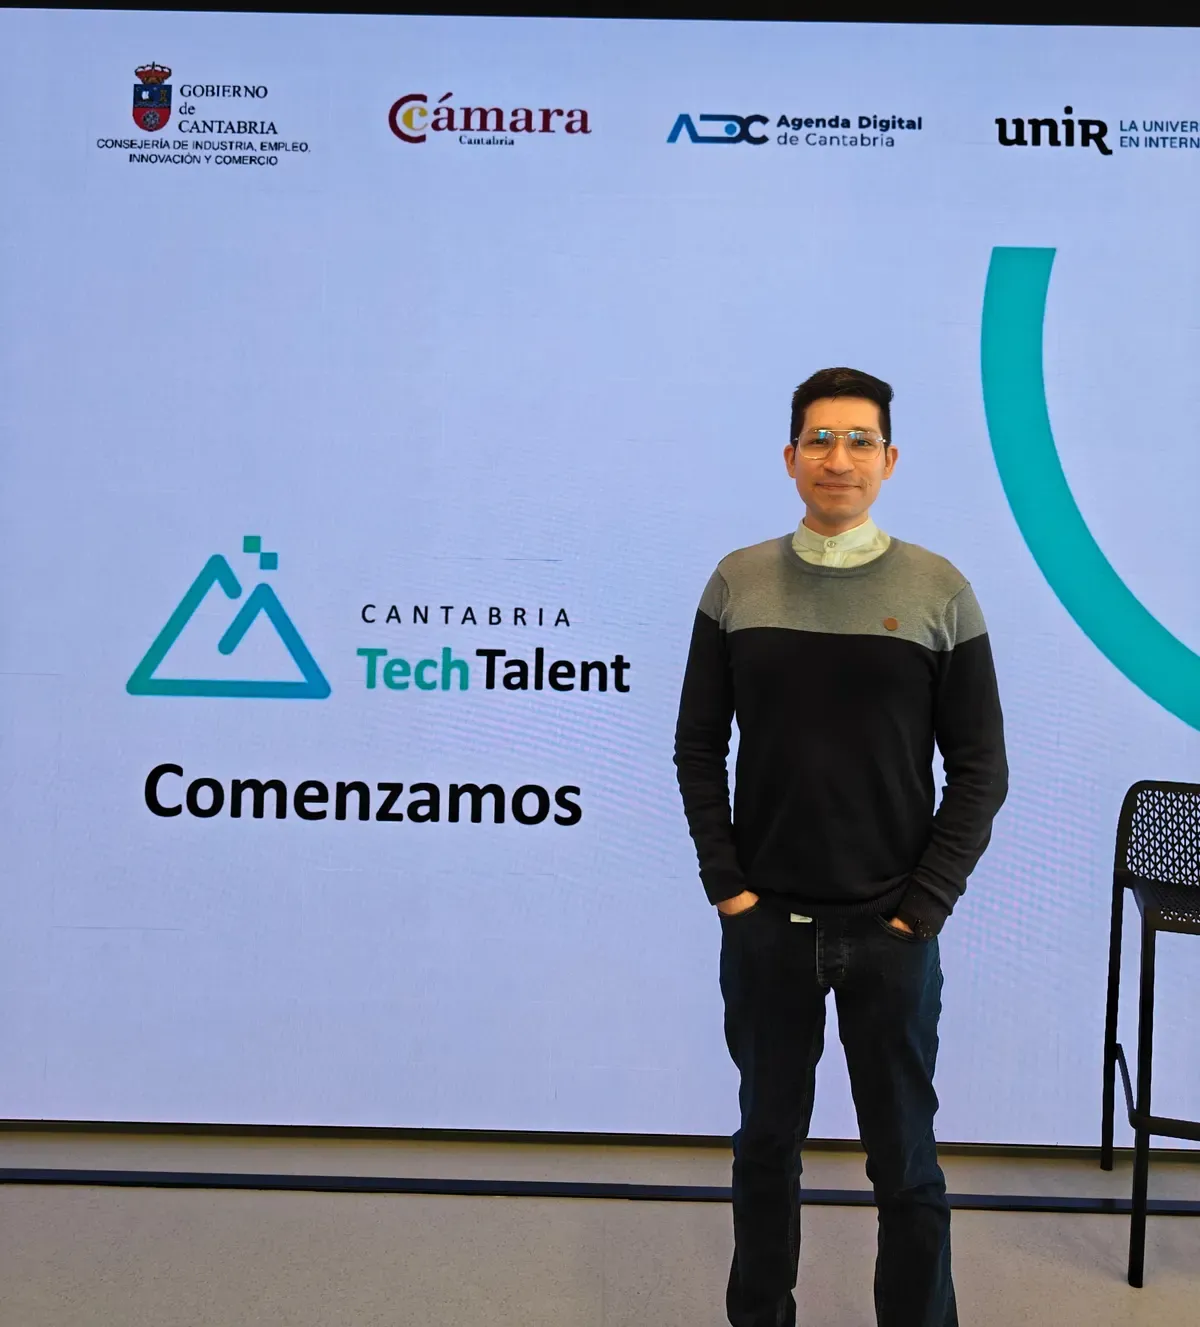
Official opening of Cantabria Tech Talent, first edition. I spoke on the panel as one of the two students.
- 68
- selected
- 1.359
- applications
- 33
- companies
Who I am
I know where you are.
If you run a small infrastructure with nobody dedicated to security, I have been on that side. I started fixing computers, today I run the security of an industrial company, and I build my tools alongside AI agents.
- More than six years in IT supportLevels 1 and 2, before security
- since 2011
- Master's in Cybersecurity and ASIR higher diplomaBoth at once. Final project submitted on 1 September 2026
- 2024 – 2026
- Cantabria Tech TalentUNIR specialisation with a work placement. One of 68 out of 1,359 applications
- first edition
- eJPTv2Entry-level certification, hands-on black-box exam
- verify
- INCIBE cyber-volunteerAwareness talks in schools and associations across Cantabria
- since 2026
What I have built
A product, a piece of research and a tool.
Product · own product · private code
Argos
Self-hosted cybersecurity platform for small companies. It brings asset inventory, vulnerability management, threat intelligence, Spanish ENS compliance, backups, device fleet and staff training into a single workflow. It is built as modules, and some stand on their own: Talos came out of it.
5,093commits between April and October 2026
Tool · open source
Talos
Hardening audit for Linux and Windows servers in a single dependency-free binary. Read-only, it never changes anything, and finishes a full server in under ten seconds. It carries 147 checks written as data files, each with its severity, weight, the Spanish ENS controls it covers and how to remediate it. It came out of a larger platform and I released it separately because it stood on its own.
<10 sper server · 147 checks
Research · CVE-2026-31431
CopyFail
A logic flaw in the Linux kernel's cryptographic subsystem lets an unprivileged local user write four controlled bytes into the page cache of any readable file on the system. That is enough to alter the behaviour of a privileged binary such as su, in memory and without touching the file on disk. It escapes containers, because they share the page cache with the host. I studied it over a long weekend, reproduced it on Debian 13, Ubuntu 24.04, Kali and Docker, and wrote variants in several languages. One of them, in C, compiles with gcc and runs on any distribution with no dependencies.
7.8CVSS · CISA KEV catalogue
Recommendations
What people say about working with me
He tenido la oportunidad de acompañar a Bray en el desarrollo de sus primeras iniciativas en ciberseguridad, y desde el inicio ha demostrado una combinación poco común de pensamiento analítico, iniciativa y creatividad para resolver problemas. A pesar de estar en una etapa temprana de su carrera, ya ha desarrollado dos proyectos propios en el área, reflejando no solo interés por la ciberseguridad sino también una fuerte capacidad de aprendizaje y ejecución. Además, destaca por su capacidad de liderazgo: sabe transmitir sus ideas, motivar a quienes trabajan con él y generar dinámicas de equipo enfocadas en encontrar soluciones. Sin duda, es un perfil con gran proyección dentro del sector.
Where I come from
Six years of IT support before security.
The security part came fast and almost all at once, between 2024 and 2026: the master's, the ASIR diploma, the eJPTv2 and Cantabria Tech Talent. Underneath there are more than six years of fixing what broke, and that is what gives me the judgement, because I know the infrastructure I defend from the inside.
Get in touch, or collaborate?
An awareness talk?
For schools, families, associations and companies in Cantabria, as an INCIBE cyber-volunteer.
Collaborate on open source?
Talos, CopyFail, the labs and whatever comes next. If you have an idea or a patch, let's talk.
A job, an audit?
Hardening, configuration review, vulnerability analysis and support with Spain's National Security Framework. Count on me.